Skip to content
Webhook reliability platform

Webhook failures, under control.

Receive authenticated webhooks, keep the event after the first failure, and see every delivery attempt. Retry with bounded backoff. Recover from the dead-letter queue with an audited replay. Your provider will keep retrying either way. You should at least know why.

Free plan available now. No credit card required. Pro is planned but not yet available for purchase.

Ingress

Signed + verified

Ack

After durable commit

Retries

Bounded + backoff

Recovery

Audited replay

Illustrative delivery lifecycle

Watch a failure recover.

Demo data · no live destination

Delivery trace

evt_8f3a · order.created

Current stage

Received

Accepted

Signature verified · durable event committed before 2xx

202 · evt_8f3a

At-least-once delivery · duplicates are possible

No live destination was harmed in this demo.

The failure is rarely the event

A missing webhook is a trail of missing state.

The provider retried. Your endpoint had a bad day. The event is somewhere between “eventually delivered” and “nobody knows” — usually in a log that was never designed for this conversation.

01

The endpoint returns 503

The provider is doing its job. Your receiver accepted the request but could not finish. The event is now waiting on a retry schedule you cannot see.

02

The retry succeeds — or does not

Without attempt-level history, “eventually delivered” and “quietly dropped” look the same from the dashboard.

03

Someone has to reassemble the state

A support ticket, a provider dashboard, and a manual replay later, the event is recovered. The next failure repeats the process.

The reliability layer

Not a queue you have to babysit.

One durable path from a verified provider request to a destination — with the evidence you need when the destination stops cooperating.

01 / Durable ingestion

Verify first. Commit before you say yes.

Provider signatures are checked against the raw request bytes. A 2xx is only returned after the event and its initial delivery job are durably committed. If storage is unavailable, the provider gets a retryable failure. A cheerful 2xx before commit is just a lie with better latency.

raw body preservedorganization-scopedno false 2xx
INGRESS PIPELINEPOST /ingest/v1/:source
  1. 01

    Read raw body

    Bytes are retained for verification and delivery.

  2. 02

    Verify signature

    Provider-specific check; no signature replay between destinations.

  3. 03

    Commit event + delivery

    Transaction completes before the 2xx response.

  4. 04

    Acknowledge provider

    Durable, scoped, observable.
RETRY WINDOWbounded
attemptdeadline

Bounded by attempts and age. Backoff is scheduled by the worker; terminal responses can move straight to dead-letter instead of retrying forever.

02 / Automatic retries

Even optimism needs a retry limit.

Transient failures are retried with backoff. Each attempt is a fresh signed request with its own timestamp. Original provider signatures are never forwarded as if they were still valid. Optimism is allowed; unbounded optimism is an incident.

Delivery is at-least-once. A retry can produce duplicates. Idempotency is still your department.

03 / Event Explorer

Every attempt, in one timeline.

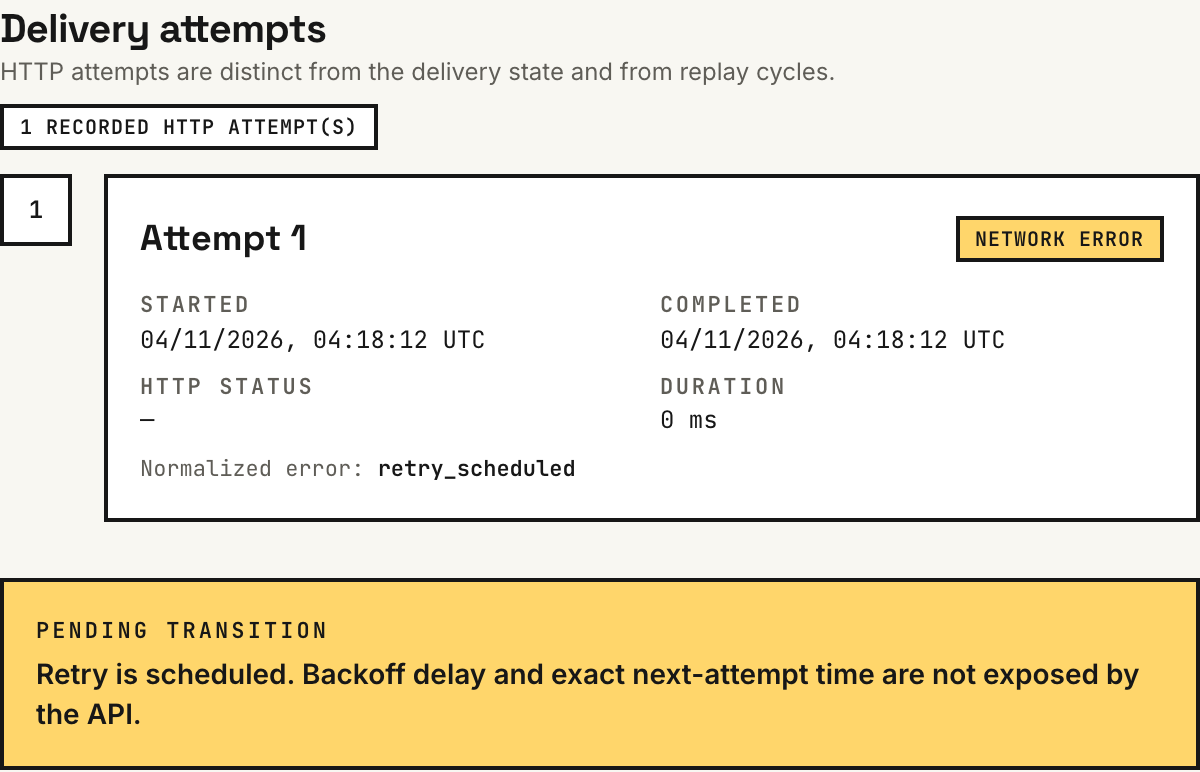
Event IDs, upstream webhook IDs, delivery identity, HTTP status, duration, normalized error. Recorded as separate facts, so “unknown” never quietly becomes “failed”. Your endpoint said 503. We kept the receipts.

Illustrative UI excerpt · no customer data

EVENT / evt_8f3aRETRYING
Illustrative delivery attempts
AttemptHTTPOutcomeDuration
01503HTTP failure1.2s
02—Unknown resultnot recorded
03200Confirmed attempt184ms

attempts ≠ delivery status ≠ replay operations

Sanitized DeadHook product screenshot showing a recorded delivery attempt with its HTTP result and normalized error

Product preview · illustrative workspace data

DEAD-LETTER / dlv_4a19REPLAY GATED

Retries exhausted.

The event is preserved. Someone with the right role can inspect the trail, write a reason, and replay it — with an explicit duplicate warning.

REPLAY REASON

Provider endpoint restored at 14:02 UTC.

audited · idempotency keyACCEPTED → QUEUED

04 / Dead-letter recovery

Dead letter. Not a dead end.

Inspect the terminal failure, fix what broke, then replay through an audited, role-gated operation. Acceptance means queued. Dead letter, not dead end. The destination still gets the final say.

At-least-once remains true through every replay.

How it works

One path. Two outcomes.

The happy path is deliberately boring. The failure path is deliberately observable. Only one of those should surprise you at 2 a.m.

01

Provider

Sends a signed webhook request

02

Verified ingress

Validates signature over raw bytes

03

Durable storage

Event + delivery job committed

04

Worker

Signs and attempts delivery

05

Destination

Your HTTPS endpoint

2xx outcome

Attempt confirmed → delivered state. At-least-once still applies.

Non-2xx / timeout / unknown

Classify → bounded retry or terminal dead-letter. Unknown results are never recorded as confirmed failures.

Developer experience

Point the provider at one URL.

No SDK to adopt, no queue to operate on day one. Create a source, copy its ingest URL, send a signed request, and let the attempt history explain the rest.

  1. 01Create a project and source
  2. 02Copy the source ingest URL into your provider
  3. 03Send a signed request — or use the provider’s webhook test
  4. 04Inspect the event, attempt, and delivery state

Your provider will not explain the 2 a.m. failure. The attempt history will.

Create a workspace →
STANDARD WEBHOOKS · SIGNED REQUESTshell
import { createHmac } from 'node:crypto';

const key = Buffer.from(
  process.env.SOURCE_SECRET.replace(/^whsec_/, ''),
  'base64'
);
const timestamp = Math.floor(Date.now() / 1000);
const id = crypto.randomUUID();
const signature = createHmac('sha256', key)
  .update(`${id}.${timestamp}.${body}`)
  .digest('base64');

await fetch(`${origin}/ingest/v1/${publicId}`, {
  method: 'POST',
  headers: {
    'webhook-id': id,
    'webhook-timestamp': String(timestamp),
    'webhook-signature': `v1,${signature}`,
    'content-type': 'application/json'
  },
  body
});
Signature format is derived from the Standard Webhooks source mode; use the provider’s documented verifier for Stripe or Shopify.

Security & delivery semantics

Trust is a property
of the system.

DeadHook is under active security and reliability verification. These are implemented controls and explicit limits — not a certification claim.

STATUS: early-stage production · no public SLA

Signed ingress

Provider-specific verification over raw bytes. No anonymous production source.

SSRF-aware egress

HTTPS and public-address validation at connect time; redirects and proxies refused where implemented.

Organization isolation

Organization data is isolated in the database and application. Access is checked for every organization-scoped request.

Secret handling

One-time secret disclosure. Raw payloads are role-gated and access is audited.

Audited replay

Role-gated recovery with an explicit reason and idempotency key; duplicate risk is stated.

At-least-once

Delivery can repeat. Consumers must be idempotent; exactly-once is not claimed.

Plans

Start small. Upgrade when the queue earns it.

The Free plan is available now. Pro is planned at $39/month plus applicable taxes and adds higher Source, Destination, member, and accepted-Event limits. Both plans include the core reliability features.

Pro is not yet available for purchase. No payment is collected today, and Paddle checkout is disabled until the Live catalog is verified. When Pro launches, paid plans will be sold by Paddle as merchant of record, in USD and excluding applicable taxes. Our Terms, Privacy Policy, and Refund Policy apply. Paddle's buyer terms will also apply to future payment transactions.

Free

Available now

$0/month

  • 3 sources
  • 5 destinations
  • 2 organization members
  • 10,000 accepted events / month shared across all your Free organizations
  • Bounded retries, DLQ, replay, and archive lifecycle

Pro

Coming soon

$39/month plus applicable taxes

  • 20 sources
  • 50 destinations
  • 10 organization members
  • 100,000 accepted events / month per Pro organization
  • Bounded retries, DLQ, replay, and archive lifecycle

Pro is planned but not yet available for purchase. No payment is collected today. Start free; upgrade will open later.

FAQ

The honest answers.

If something is missing, it stays missing from this list. Marketing is allowed to be optimistic; the product list is not.

Which providers are supported?

Source verification currently supports Standard Webhooks, generic bearer tokens, Stripe signatures, and Shopify HMAC. Availability and behavior are provider-specific; confirm the verifier you need before sending production traffic.

What are the retry policies?

Retries are bounded by attempt count and age, with scheduled backoff. Terminal responses can move directly to the dead-letter queue. These are product limits, not a guarantee of delivery.

How are webhook signatures handled?

Inbound requests are verified against the configured source mode using the raw body. Outbound deliveries are re-signed with DeadHook’s own Standard Webhooks signature and a fresh timestamp; original provider signatures are not forwarded as still-valid.

What does replay mean here?

A replay is an audited, role-gated operation that re-queues a dead-lettered delivery with a required reason and idempotency key. Acceptance means queued — not that the destination has already received the webhook.

Do you deduplicate events?

DeadHook does not currently promise exactly-once or provider-wide deduplication. Delivery is at-least-once, and consumers should use idempotency keys from the provider where available.

How do I start?

Create a workspace, project, and source, add an HTTPS destination, then send a signed request to the source ingest URL. The onboarding guide walks through setup and verification states using real workspace data.

Is this production-ready?

DeadHook is live as an early-stage production service. The Free plan is available now. We do not offer a public uptime SLA or third-party certification. Pro is planned and is not yet available for purchase.

Build the recovery path before you need it

Make the next failure
an incident you can inspect.

Free plan available · registration open